
MTTD and MTTR measure two things every security leader is accountable for: how long a threat goes unnoticed, and how long it takes to contain once found. Every day in that window adds cost, and the window is getting longer, not shorter.
Faster detection and containment is also one of the few security improvements that can be measured, reported and proven to a board, regulator or insurer.
This guide covers the formulas, current benchmarks, and the specific steps a security operations center (SOC) uses to bring both numbers down, then shows how to report them to boards, regulators and insurers.
Mean time to detect (MTTD) is the average time between an intrusion beginning and the SOC confirming it as a real incident. Mean time to respond (MTTR) is the average time from that confirmation to containment. Together they form the total exposure window: how long an attacker has to operate inside your environment.
Some industry studies use related terms: mean time to identify (MTTI) for the detection window and mean time to contain (MTTC) for the response window. The benchmarks below use both sets of terms.
An MTTD or MTTR figure is only useful if its start and end points are documented and held constant over time.
There is no universal target; a good MTTD and MTTR depends on your industry, threat profile and SOC maturity. The two most cited industry studies give useful reference points, but they measure different things, so read them together.
| Measure | 2026 Figure | Prior Year | Source |
|---|---|---|---|
| Mean time to identify and contain a breach | 247 days | 241 days | IBM Cost of a Data Breach Report 2026 |
| Mean time to identify a breach | 183 days | 181 days | IBM Cost of a Data Breach Report 2026 |
| Mean time to contain a breach | 64 days | 60 days | IBM Cost of a Data Breach Report 2026 |
| Global median dwell time, targeted attacks | 14 days | 11 days | Mandiant M-Trends 2026 |
| Median dwell time, cyber espionage and North Korean IT worker intrusions | 122 days | Not reported | Mandiant M-Trends 2026 |
| Median time from initial access to hand-off to a second threat group | 22 seconds | Over 8 hours (2022) | Mandiant M-Trends 2026 |
IBM reports a mean across 602 breached organizations, so a small number of very long breaches pull the figure up. Mandiant reports a median across the targeted intrusions its consultants investigated. Both moved in the wrong direction this year, which makes the trend more important than either number.
The last row matters most for MTTR. When an initial access broker can hand a foothold to another threat group, such as a ransomware operator, in seconds, a response measured in hours leaves the attacker ample time to act.
Set MTTD and MTTR targets by incident severity, not as a single average. A critical ransomware or privileged access incident needs a far tighter target than a low-severity policy violation.
In IBM’s 2026 data, breaches with lifecycles over 200 days cost an average of $5.65 million, against $4.32 million for those resolved sooner. Financial services breaches cost an average of $6.3 million. Organizations using security AI and automation extensively averaged $1.93 million less per breach and identified and contained breaches 65 days faster (215 days against 280).
Benchmark against your own trend line first and industry figures second; both major studies show detection getting slower in 2026.
Reducing MTTD is about visibility and signal quality: the SOC must see the right data, and real threats must stand out from the noise. Five practices do most of the work.
MTTD falls when the SOC sees more of the environment and spends less time on noise.
Where MTTD is a visibility problem, MTTR is a process problem. The clock runs from confirmation to containment, and delay builds at decision points and handoffs.
MTTR falls when decisions are made before the incident, not during it.
247 Days to Find and Contain a Breach. Yours Should Be Measured in Hours.
The WICS SOC monitors, investigates and contains threats around the clock, with MTTD and MTTR reported to you every month.
MTTD and MTTR turn security performance into evidence that non-technical stakeholders can follow: a consistent downward trend shows that controls are working, where an alert count shows only activity.
For US-listed companies, the SEC cybersecurity disclosure rule adds direct time pressure. Form 8-K Item 1.05 requires disclosure of a material cybersecurity incident within four business days of determining that it is material, and Regulation S-K Item 106 requires annual disclosure of cybersecurity risk management processes and board oversight. Slow detection and escalation delay the materiality determination itself.
Report trends, not snapshots. A quarterly view should show:
| Item | What to Show | Why It Matters to the Board |
|---|---|---|
| MTTD by severity | Median and mean, last four quarters | Shows whether threats are found faster |
| MTTR by severity | Median and mean, last four quarters | Shows whether damage is contained faster |
| Critical incidents | Count, with time to contain for each | Connects metrics to real events |
| Improvement actions | What changed and its effect on the metrics | Shows return on security investment |
The question for the board shifts from “how many alerts did we close?” to “how fast did we detect and contain the ones that mattered?”
Work through these seven actions in order; the first two make every later improvement measurable.
Both major industry studies show detection getting slower in 2026, while attackers move from initial access to impact faster than ever. Organizations that define, measure and steadily reduce MTTD and MTTR shrink that exposure window and can prove it to their boards, regulators and insurers. Those that keep counting alerts will not know how exposed they are until an incident tells them.
This FAQ seeks to answer some of the most common questions and confusions about this topic.
MTTD measures the time to detect a threat; MTTR measures the time to contain and remediate it once detected. Combined, they equal an incident’s total dwell time.
For critical threats, leading SOCs target containment in under four hours. Less mature programs often measure MTTR in days. Set targets per service tier rather than as one organization-wide figure.
Sum the detection time across all incidents in a period, then divide by the number of incidents. Track the median alongside the mean so long-dwell outliers do not distort the picture.
Frameworks such as NIST CSF 2.0 and the SEC disclosure rules expect demonstrable evidence of effective controls. Trending these metrics gives auditors, boards, and cyber insurers concrete, data-driven proof of due diligence.
Automation delivers the fastest gains. SOAR-driven triage, alert enrichment, and pre-approved containment actions remove manual delay without adding headcount.
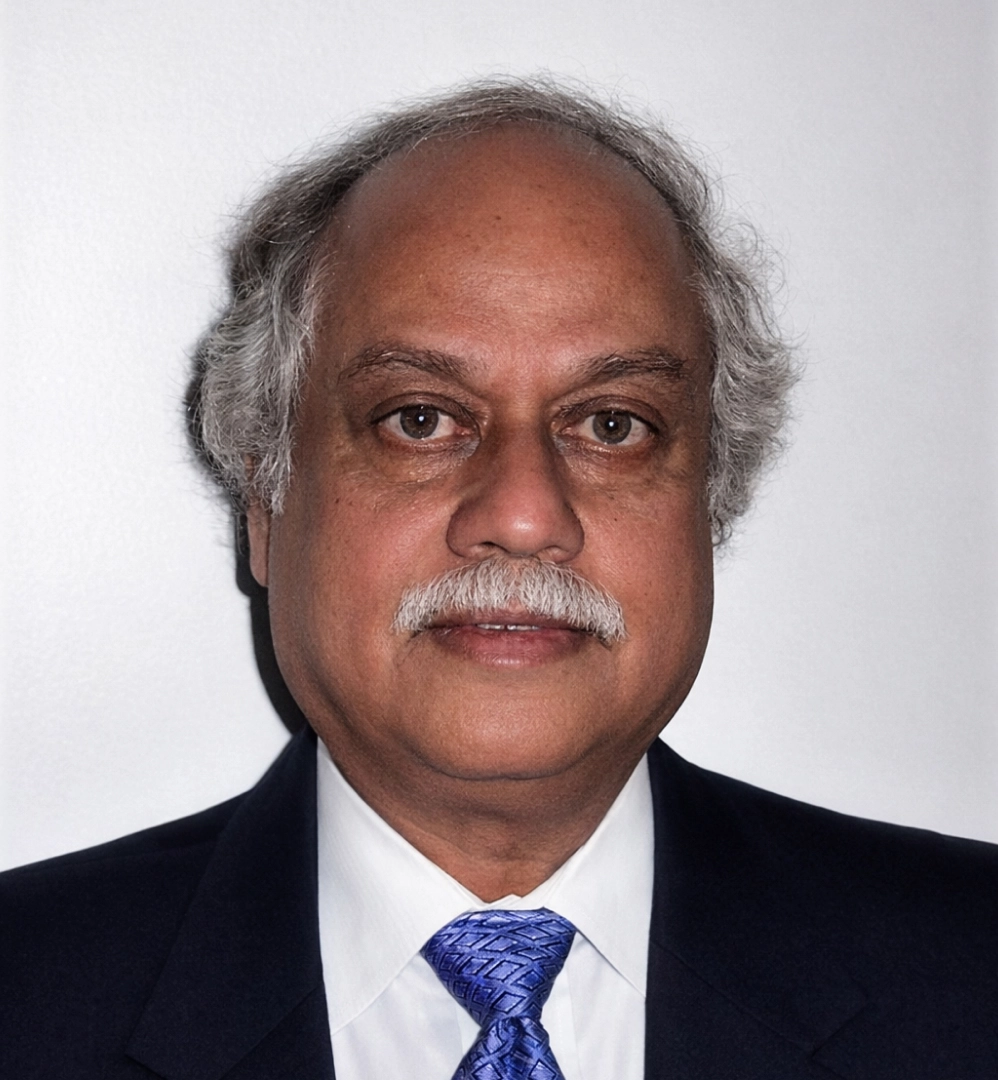
Rakesh Asthana is the founder of World Informatix Cyber Security and a veteran technology and security leader with over 40 years of experience safeguarding complex global institutions. As a former Senior IT Director and CIO for the World Bank, he led large-scale IT and cybersecurity transformations, strengthening resilience across highly regulated environments. Notably, he played a pivotal role in the incident response and digital forensics during the Bangladesh Bank cyber heist. This experience continues to shape his pragmatic, risk-driven approach to securing financial systems worldwide.

